Key Takeaways
- A surveillance audit samples the management system rather than re-examining all of it, so the areas a registrar must revisit every cycle deserve the most preparation.
- Closed findings, a completed internal audit program and a documented management review are the three records auditors ask for first.
- Corrective actions are judged on root cause and effectiveness, not on whether a form was signed.
- Frontline staff who can explain their own process calmly do more for the result than a perfect binder.
The week before the registrar arrives is the wrong time to find out that an internal audit was skipped or a corrective action never got verified. An ISO surveillance audit preparation checklist works best when it is used months ahead, so gaps become scheduled work instead of last-minute scrambles. The nine points below follow the order in which auditors usually test a manufacturing quality system, starting with the records and ending with the people.
Understanding the Scope and Focus of an ISO Surveillance Audit
A surveillance audit is the periodic visit a certification body makes between the initial certification and the recertification audit, and it is usually scheduled once a year. The auditor does not retest every clause. Instead, the visit samples the system, always returns to a fixed set of items, and follows up on anything found previously.
That is the main difference from a recertification audit, which looks at the whole system again at the end of the certificate cycle. If you want to see how the earlier audits split the work, the article on ISO certification audit Stage 1 vs Stage 2 explains what the first two audits check.
One point of context: ISO 9001:2026 is the current edition, and many certified organizations are still on ISO 9001:2015 during the three-year transition ending in September 2029. The clause numbers in this article refer to ISO 9001:2015, and the same records are what auditors ask for under either edition.
Did You Know? Certification bodies in Canada are accredited by the Standards Council of Canada, which is why a registrar's audit method follows a defined, checked process. The accreditation program is public.
Point 1: Verify Closure and Effectiveness of Prior Audit Findings
Start with every finding from the last audit, major or minor. The auditor will open the report and ask to see what was done. Closure alone is not enough, because the registrar also wants proof that the fix worked.
Check each finding for three things:
- The action addressed the cause the team identified, not just the symptom that was noticed.
- Someone other than the person who made the change reviewed the result.
- The evidence shows the problem has not returned since.
An open finding carried into the visit is one of the quickest ways to turn a minor nonconformity into a major one.
Point 2: Ensure Completion of the Annual Internal Audit Schedule
Clause 9.2 of ISO 9001:2015 requires internal audits at planned intervals, and the auditor will compare the schedule with what actually happened. A plan that lists twelve audits but shows eight reports invites questions.
If the schedule slipped, finish the missing audits before the visit rather than explaining the gap. The 12-point internal audit checklist for manufacturing plants is a useful starting point when audit questions need tightening. Auditors read internal audit reports closely, because shallow reports tell them how seriously the system is run.
Point 3: Hold and Fully Document an Executive Management Review
Clause 9.3 of ISO 9001:2015 expects top management to review the system at planned intervals, and the records must show that real decisions were made. Minutes that only restate the agenda tend to draw a finding.
A management review record should cover the inputs the standard lists, in words that match your plant:
- Status of actions from earlier reviews.
- Changes in issues that affect the system.
- Performance information, including audit results and customer feedback.
- Decisions on improvement, resources and any needed system changes.
Hold the meeting with the plant manager or owner in the room, because an auditor will ask them what was decided.
Point 4: Measure Performance Metrics Against Stated Quality Objectives
Clause 6.2 of ISO 9001:2015 requires measurable quality objectives, and the auditor will ask where each one stands. Pull the latest figures from your own records for on-time delivery, scrap, rework and customer returns, then compare them with the targets.
An objective that was missed is not a problem by itself. A missed objective with no analysis and no action is. Be ready to show what the team learned and what it changed.
Key Consideration: Keep each objective tied to a named owner and a source of data, so the answer to "where does this number come from?" takes seconds rather than a search through spreadsheets.
Point 5: Document Management System Changes and Scope Adjustments
A new product line, a second shift, a moved machine or a changed supplier can all affect the system. Clause 6.3 of ISO 9001:2015 asks that changes be planned, and the certification body expects to hear about changes to scope or location.
Write a short change summary covering what changed, who assessed the effect on quality, and which documents were updated. If the scope statement no longer matches what the plant does, correct it before the visit and tell the registrar. Surprises on the floor that contradict the scope are hard to explain.
Point 6: Review Corrective Action Logs for Root-Cause Integrity
Clause 10.2 of ISO 9001:2015 requires corrective action that deals with the cause of a nonconformity. Auditors sample the log and read the root-cause entries, looking for patterns such as "operator error" or "retrained employee" repeated as the answer to different problems.
Corrective action verification matters here: each closed entry should show a check, dated after the fix, that the problem did not return. If several entries point to the same weak cause, strengthen the analysis with a method such as five whys or a cause-and-effect diagram before the visit. Weak root-cause work is among the more common reasons an auditor widens the sample.
Point 7: Compile Customer Feedback, Scorecards, and Complaint Data
Clause 9.1.2 of ISO 9001:2015 asks the organization to monitor customer perception. For a manufacturer, that usually means supplier scorecards from buyers, complaint and return records, and any customer audit results.
Gather them in one place and show how they feed the management review and the objectives. If a customer scorecard shows a downward trend, the auditor will want to see an action plan. Showing the trend and the response is far better than hoping nobody asks.
Point 8: Audit Shop-Floor Workstations, Calibrations, and Revision Control
Auditors leave the conference room, and what they see on the floor must agree with the paperwork. Walk the plant the way a registrar would, with these checks:
- Gauges and measuring equipment carry a valid calibration label, and the calibration record is traceable to a recognized standard (clause 7.1.5 of ISO 9001:2015).
- Work instructions at each station are the current revision, with obsolete copies removed.
- Nonconforming material is identified and segregated.
- Product and material identification matches the traveler or work order.
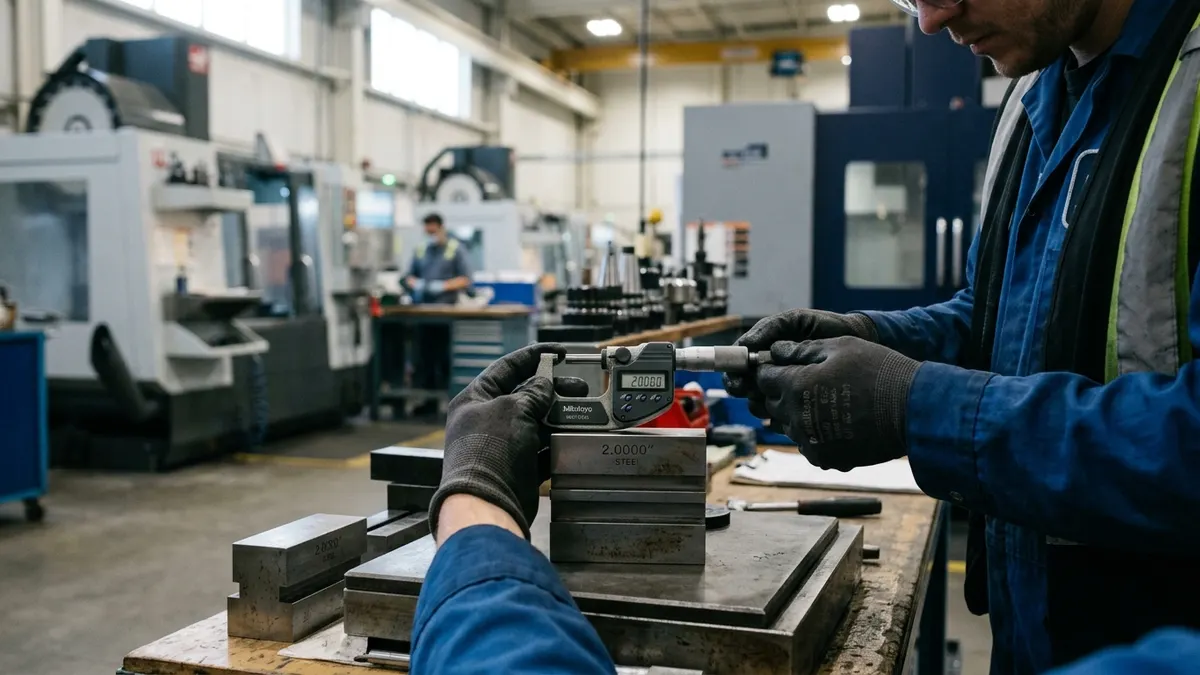
Problems found here are usually easy to fix, which makes them the cheapest findings to prevent.
Point 9: Coach Process Owners and Frontline Staff on Auditor Interviews
Auditors interview operators, supervisors and process owners, and these answers carry weight. The goal of coaching is not to rehearse scripts. It is to make sure people can explain what they do, where their instructions live, and what they do when something goes wrong.
Tell staff that it is fine to admit when an answer is not known, as long as they can show where to find the information. Answering a question that was not asked, or guessing, is where interviews usually go wrong. A short walk-through of the quality policy and each person's role helps more than a long briefing.
Important: Staff should be told to answer only the question asked and to show records when they have them. They should never be told to hide a problem, because a concealed nonconformity found later is treated far more seriously than an openly handled one.
Common Surveillance Audit Traps That Trigger Major Nonconformities
A few patterns recur in plants that struggle at this stage, and each one connects to a point above:
- An internal audit program that stopped after the certificate was issued, with nothing to show for a long stretch.
- A management review held on paper only, with no decisions and no executive involvement.
- Corrective actions closed without verification, so the same issue returns in the next audit cycle.
- Out-of-date work instructions at the point of use.
Any of these can lead an auditor to question whether the system is being maintained, and a registrar may raise a major nonconformity when a whole requirement is not being met. Detail on how certificates are granted and kept is given in ISO's own explanation of ISO 9001.
Quick-Reference Summary
Use this list as a final pass in the weeks before the visit:
- Confirm that every earlier finding is closed and verified.
- Complete the internal audit schedule and file the reports.
- Hold the management review and record decisions.
- Update objectives with current data.
- Summarize system and scope changes.
- Test corrective action entries for root cause and follow-up checks.
- Collect customer feedback and scorecards.
- Walk the floor for calibration, revision control and identification.
- Coach staff on interviews.
Frequently Asked Questions
How often do ISO surveillance audits occur after initial certification?
Surveillance audits are typically held once a year during the three-year certificate cycle, with the recertification audit closing the cycle. Some certification bodies schedule them at shorter intervals when a plant has a record of serious findings.
What happens if an external auditor discovers a major nonconformance during a surveillance audit?
The certification body will require a corrective action plan within a set period and will normally verify it, sometimes with a follow-up visit. The certificate can be suspended if the issue is not resolved.
How does an ISO surveillance audit differ from a full recertification audit?
A surveillance audit samples the system and revisits fixed items, while a recertification audit reviews the whole system again to renew the certificate for another cycle.
Can an organization lose ISO certification during an annual surveillance audit?
Yes, in principle. Certification can be suspended or withdrawn if serious nonconformities are not corrected within the time allowed or if the system is no longer being maintained.
How many days on-site does an ISO surveillance audit typically take for a manufacturing plant?
The length depends on the number of employees, the scope and the complexity of the processes, and the certification body sets it. Smaller plants usually need fewer audit days than multi-site operations.
A plant that wants a second opinion before the registrar arrives can start with the free ISO readiness assessment to see which clauses need attention. ISO Certification Consultants work with Ontario manufacturers to review records, walk the floor and prepare staff, and a conversation through the contact page is the simplest way to plan that work.